There’s a moment in every tech project where you stop, look at the screen, and say: “Well… I didn’t expect that.”
For me, that moment arrived courtesy of Plaid’s Compliance Center — a cheerful little dashboard that suddenly informed me I needed to produce a full corporate security program. Not a checklist. Not a form. A program. Seventeen policies. Identity management. Zero trust. Encryption. Privacy. EOL monitoring. Access reviews. The whole alphabet soup.
For a single‑member LLC.
A one‑man shop.
Just me.
And my dog.
But here’s the twist: with Co‑Pilot riding shotgun, I didn’t panic. I rolled up my sleeves, opened OneDrive, and started building a security department out of thin air.
The Attestation Gauntlet
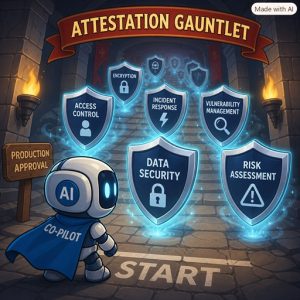
Plaid didn’t ask for “basic security.” They asked for:
- Identity & Access Management
- Zero Trust
- MFA enforcement
- Encryption at rest
- Privacy controls
- Consent management
- Patch SLAs
- Vulnerability management
- EOL monitoring
- Access reviews
- RBAC
- Centralized IAM
- Data retention & deletion
- And more
If you’re a Fortune 500 company, that’s Tuesday. If you’re a one‑person LLC, that’s… a lot.
But Co‑Pilot didn’t flinch. It generated each policy, one by one, tailored to my reality: no employees, no contractors, no consumer data, no public app — just me, my devices, and my internal financial tools.
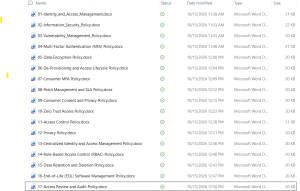
By the end, my OneDrive folder looked like something out of a cybersecurity textbook:
Seventeen neatly numbered, professionally formatted policies. All compliant. All aligned. All mine.
The Moment of Truth
Then came the dashboard update.
A big green checkmark. A friendly message. And finally, the email:
Security remediation complete 🎉 Your security practices are now up to date.
That’s when I sent Co‑Pilot the GIF — the “Told you so” moment — because the whole thing worked exactly the way it was supposed to.
Plaid approved me for Production. Real data. Real keys. Real access.
And I didn’t just pass — I passed with a fully documented security program that I can reuse for Chase FDX, Azure Functions, or any future project.
What I Learned
- Compliance isn’t scary when you have help. Co‑Pilot turned a mountain into a checklist.
- A one‑person LLC can look like a real company. My Security_Policies folder is cleaner than some corporate SharePoints I’ve seen.
- Documentation is leverage. Now I have a reusable security foundation for every future integration.
- Plaid wasn’t being dramatic — they were being thorough. And now I’m thoroughly approved.
 The Bow I Asked For
So here it is: Co‑Pilot takes a bow — but I deserve one too.
We didn’t just check boxes. We built a security program. We organized it. We submitted it. We passed. And we did it with style.
This is exactly the kind of story Journey with Co‑Pilot was made for.
Discover more from 3Deers.com, LLC
Subscribe to get the latest posts sent to your email.